AI SIEM Defined in Plain Terms
An AI SIEM is a security information and event management platform that adds machine learning and behavioural analytics to the usual job of collecting and correlating log data. It still gathers events from across your systems but it also learns what normal looks like, scores anomalies and automates parts of detection and response so analysts see fewer, better alerts.
The reason this matters is volume. A mid-sized organisation produces more log data every day than any team can read and attackers now use automation of their own. ENISA analysed 8,257 cyber incidents recorded across the EU in 2025 and documents the growing use of AI in malicious operations (ENISA Threat Landscape 2026). A rules-only SIEM that waits for a known pattern is working against that tide.
Vendors also market the same idea as next-generation SIEM, AI-based SIEM or machine-learning SIEM. The label varies. The core shift does not. It is a move from fixed rules towards models that can flag behaviour no one wrote a rule for.
How an AI SIEM Works
An AI SIEM runs the same pipeline a traditional SIEM does, with an analytics layer added on top. It helps to follow a single event through it.
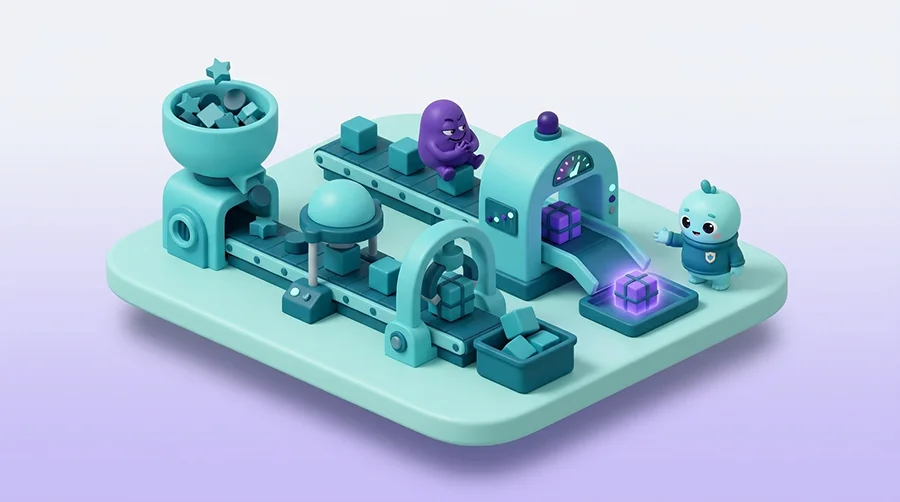
- Collection: It ingests logs from endpoints, servers, network devices, identity systems and cloud services into one place.
- Normalisation: It converts those different formats into a common structure so events can be compared.
- Correlation: It links related events across sources into one picture rather than a stream of isolated lines.
- Detection: Alongside fixed rules, machine-learning models and behavioural baselines score how unusual an event is.
- Triage and response: The platform ranks what matters, enriches it with context and can trigger an automated action such as isolating a host.
Two things made this practical. Cloud platforms made it cheap to store and process very large volumes of data, and anomaly-detection techniques matured enough to run on security telemetry. That is what lets a modern SIEM learn a baseline for each user and device instead of relying only on rules written in advance.
What an AI SIEM Adds to a Traditional SIEM
A traditional SIEM is mostly a search and alerting engine over your logs. An AI SIEM keeps that and adds five capabilities that change what a small team can cover.
- Behavioural analytics (UEBA): User and entity behaviour analytics builds a profile of normal activity for each account, host and service, then flags deviations such as a login at an odd hour from a new location.
- Anomaly detection: Models score events by how far they sit from the baseline which surfaces threats that match no known signature.
- Alert correlation and noise reduction: Related alerts are grouped into one ranked incident so analysts chase a handful of real cases instead of thousands of raw alerts.
- Automated investigation and response (SOAR): The platform gathers context automatically and can run a predefined action, for example disabling an account or isolating a device.
- Threat-intelligence enrichment: Incoming events are matched against known indicators and risk scored, so a suspicious item arrives with context attached.
None of this is magic. Each capability is only as good as the data feeding it which is where most deployments succeed or fail.
Why AI SIEM Matters Now
The case for AI in the security operations centre rests on a gap between the work and the people. ISC2 estimated the world needs about 4.8 million more cybersecurity professionals than it has (ISC2 Cybersecurity Workforce Study, 2024). Most teams cannot hire their way out of alert volume so they have to reduce it.
Alert fatigue is the direct risk. When a SIEM produces thousands of low-value alerts a day, the one that matters gets lost. Reducing and ranking alerts is the difference between noticing an intrusion and missing it.
The second risk is dwell time, the stretch between a breach starting and anyone noticing. Long gaps turn a contained incident into a disclosed one with regulatory and recovery costs attached and gaps of weeks or months are common.
In Sweden the dependency risk is concrete. In August 2025 a ransomware attack on the HR software supplier Miljödata disrupted services for about 200 of the country’s 290 municipalities (Swedish press agency TT, August 2025). When one supplier can affect that many bodies at once, the ability to detect unusual activity early, across your own systems and your suppliers’, becomes a practical requirement.
Real-World Cases
Three well-documented breaches show three ways monitoring fails and what an AI SIEM is meant to fix in each.
Target, 2013: The Alert That Was Not Acted On
In late 2013 attackers stole about 40 million payment card records, along with personal data on up to 70 million customers from the US retailer Target (US Senate Committee on Commerce, 2014).
The striking detail is that Target’s monitoring worked. Its malware detection flagged the exfiltration tool and raised alerts, which staff saw and did not escalate.
An AI SIEM is built for this failure. Correlating those detections into a single high-severity incident, ranking it above the daily noise and paging an on-call analyst is the control that closes the gap between an alert and an action.
Equifax, 2017: The Sensor That Went Blind
In 2017 attackers accessed the personal data of at least 145.5 million people from the credit bureau Equifax, and went undetected for 76 days (US Government Accountability Office, 2018).
A device that inspected encrypted network traffic had been running with an expired certificate for about ten months, so it quietly stopped inspecting traffic. The moment Equifax renewed the certificate, the tool saw the suspicious activity and the company blocked it.
The lesson here is about coverage, not cleverness. A monitoring platform should watch its own health and raise an alarm when a log or traffic source goes silent. A blind sensor is itself an incident and a SIEM that tracks data-source health would have surfaced the gap long before day 76.
Capital One, 2019: The Anomaly No One Flagged
In 2019 a single attacker took data on about 106 million people from the bank Capital One including roughly 140,000 US Social Security numbers (Capital One disclosure and US Office of the Comptroller of the Currency, 2020).
The attacker used a web-application flaw to obtain cloud credentials, then used those credentials from an outside address to copy about 30 gigabytes from storage. Capital One did not catch any of this through its own monitoring. An outside tip, roughly four months later, is what surfaced the breach.
Behavioural analytics answers this pattern directly. A baseline of normal activity would have treated a service account’s credentials appearing from an unfamiliar location followed by a bulk data transfer, as two anomalies worth escalating rather than routine noise.
AI SIEM and Compliance
Detection is not only an operational choice in the EU. Several regimes now require continuous monitoring and fast reporting and you cannot report what you did not detect.
NIS2 and Cybersäkerhetslagen: The EU NIS2 Directive is in force in Sweden as Cybersäkerhetslagen (SFS 2025:1506) since 15 January 2026. Article 21.2a requires continuous monitoring and Article 23 requires incident reporting, with an early warning within 24 hours and a full notification within 72 hours. Since 1 July 2026 these reports go to the National Cybersecurity Centre (NCSC) at FRA, through CERT-SE, rather than to MCF. Under Article 20 the board can be held personally accountable. See our NIS2 compliance guide for the full duties.
DORA: For financial entities, the Digital Operational Resilience Act requires ICT incident management and reporting under Article 17, supervised by Finansinspektionen. Detection and classification of incidents is the first step the regulation assumes you can perform. Our DORA compliance guide covers the detail.
GDPR: Article 33 requires notifying the Swedish data protection authority, IMY, within 72 hours of becoming aware of a personal-data breach. Awareness depends on detection so a monitoring gap directly threatens this deadline. The Miljödata attack is itself the subject of an IMY investigation. See our GDPR compliance guide.
ISO 27001: The 2022 version of the standard makes logging (control 8.15) and monitoring of activities (control 8.16) explicit parts of an information security management system. An AI SIEM is a common way to satisfy both. Our ISO 27001 guide explains the certification.
One point sits under all of these. A SIEM processes your most sensitive logs, so where that processing happens matters. Under the Schrems II ruling (CJEU, 2020) and the US CLOUD Act, a provider subject to foreign government access can be compelled to hand over data stored in the EU. For a Swedish essential entity, the jurisdiction of the SIEM provider is a question to ask before the features.
How to Evaluate an AI SIEM
If you are comparing platforms, a few questions separate a useful AI SIEM from an expensive dashboard.
- Data coverage: Can it ingest every log source that matters including your cloud and identity systems, and does it alert when a source goes silent?
- Explainability: When a model flags something, does it show why or is the alert a black box an analyst cannot defend?
- Tuning burden: How much work is needed to baseline your environment and keep false positives down, and who does that work?
- Integration and response: Does it connect to the tools you already run and can it trigger a real response rather than only raising a ticket?
- Data residency: Where are your logs processed and stored and is the provider subject to foreign access laws?
The honest caveat is that AI does not run a SOC on its own. A model is only as good as the data it learns from. It can be fooled by an attacker who moves slowly, and its alerts still need a person to judge and act on them. The value is a smaller team covering more ground with less noise. It is not a system you can leave unattended.
How to Get Value from an AI SIEM
Getting value from an AI SIEM is mostly about how you run it across people, process and technology.
- Get your log coverage right first. A model cannot find what it never sees so connect your critical sources before you judge the detections.
- Alert on silence. Treat a log source that stops reporting as an incident to investigate.
- Baseline, then tune. Let the platform learn normal activity, then cut the false positives down so the real alerts stand out.
- Keep a human in the loop. Route the ranked, high-confidence alerts to an analyst who can decide and respond.
- Pair detection with response. Detection only pays off if it leads to action, whether through your own team or a managed service.
- Check where your data lives. Confirm the processing location and the provider’s jurisdiction before you sign.
Many organisations do not run this in-house. A managed detection and response service applies the same discipline with analysts watching around the clock, and keeps the response attached to the alert. If you are weighing that option, our managed detection and response service and AI detection and response service describe how eBuilder runs it.