OSINT Explained in Plain Terms
OSINT, short for open-source intelligence, is the practice of collecting and analysing information from publicly available sources. In cyber security it describes how an attacker researches a target using social media, company websites, public records and leaked data, long before sending a single email or making a single call.
The information is public, so gathering it breaks no system and sets off no alarm. That is what makes OSINT the quiet first move behind most targeted attacks. The richer your public footprint, the easier it is for someone to impersonate a colleague, reuse a leaked password or write a message you are likely to trust.
In Swedish the same idea is called information från öppna källor. Whatever you call it, the lesson holds. Your people are researched well before they are attacked, and knowing that is where the defence begins.
How Attackers Gather OSINT
Reconnaissance is the first stage of an attack. In the MITRE ATT&CK framework, the reconnaissance tactic covers the techniques an adversary uses to gather information before trying to get in. It sits ahead of initial access for a reason. Good research is what makes the later steps work.
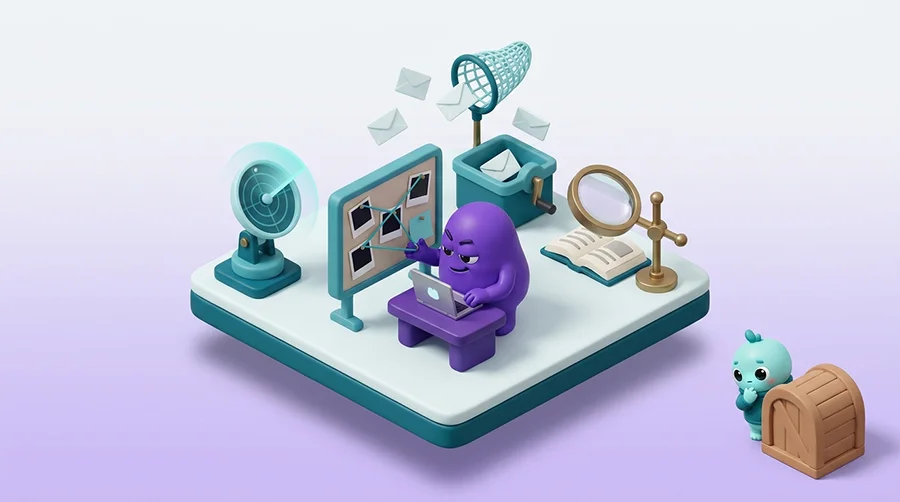
Most of it is passive. The attacker reads what is already published and takes nothing from you directly. MITRE catalogues this as gathering victim identity information, gathering victim organisation information and searching open websites and social media. In plain terms that means your staff list, your reporting lines, your email format and anything your people post in public.
Some of it is active, meaning the attacker interacts with you to learn more. A probing email that asks an innocent question, a call to reception, a quiet look at your login page. MITRE calls the email version phishing for information.
OSINT tools make the passive work fast. Search engines with advanced operators surface documents you forgot were public. Shodan maps internet-exposed devices and services. theHarvester and SpiderFoot gather email addresses, subdomains and staff names automatically. Maltego then draws the links between the people and the systems they use. Have I Been Pwned shows which of your addresses appear in known breaches.
None of these tools is sinister on its own. Defenders use the same ones to audit their own exposure. The difference is intent. Running them against your own organisation is the fastest way to see what an attacker already sees.
Your OSINT Attack Surface
Your attack surface is not only servers and software. It is also every public trace of your organisation and the people in it. Each source below is something an attacker reads, and most of it is put there by the business itself.
- Social media and LinkedIn: The single richest source. Roles, reporting lines, new joiners, projects and who is covering for whom, all in one place.
- Job adverts: A vacancy that names your firewall, your EDR or your cloud platform tells an attacker exactly what to prepare for.
- Out-of-office replies: An automatic reply that a finance manager is away until Monday is an invitation to impersonate them.
- Breach and data-broker records: Old breaches expose reused passwords, and brokers sell phone numbers tied to names. This is how a text reaches the right employee.
- Document metadata: Files published online can carry author names, internal paths and software versions in their properties.
- Websites and DNS: Subdomains, staff portals and technical records sketch the shape of your network from the outside.
- Photos and videos: A team photo can reveal a badge design, a desk shot can reveal a screen, an office tour can reveal the building layout.
Social media is where this adds up fastest. Any one post is harmless. A hundred of them, read together, become an org chart, a routine and a shortlist of people worth targeting.
The Business Impact of OSINT-Driven Attacks
Reconnaissance has no real cost of its own. The cost arrives in what it enables. Research turns a generic scam into a tailored one, and tailored messages are far more likely to work.
Phishing was the primary way into EU organisations in the ENISA Threat Landscape 2025, around 60 percent of observed intrusions. OSINT is what lifts a phishing email from obvious junk to a message that names your manager and refers to a real project.
The money follows the same path. Business email compromise, where an attacker impersonates an executive or a supplier to redirect a payment, cost 3.05 billion dollars across 24,768 complaints reported to the FBI in 2025. That made it the second costliest category of cybercrime the FBI tracked that year, and every case began with research into who authorises payments and who they answer to.
The same research feeds several kinds of attack.
- Spear phishing: A targeted email built from real names, projects and relationships.
- Vishing and smishing: Calls and texts that use knowable facts to sound legitimate, often aimed at the help desk.
- Credential attacks: Leaked passwords tried against your logins, because people reuse them.
- Impersonation and BEC: A fake executive or supplier request that fits a real deal.
- Physical intrusion: A visitor who name-drops the right people and the right project to get through the door.
Artificial intelligence has sharpened all of this. By early 2025, AI-assisted phishing made up more than 80 percent of observed social engineering activity, according to ENISA. Research that once took hours can now be automated and written up in flawless Swedish or English.
Real-World Cases
Three incidents show the same pattern. Research on people comes first, then a person is tricked into opening the door.
The 2020 Twitter Breach
In July 2020, attackers phoned Twitter employees while posing as the company’s IT staff and steered them to a fake login page. Having harvested credentials, they found employees with access to internal account tools and took over 130 high-profile accounts to run a Bitcoin scam that collected about 118,000 dollars.
The New York State Department of Financial Services investigated and found that more than a thousand employees could reach those internal tools. The reconnaissance was easy because the target was broad.
Two controls would have blunted it. Far fewer people should hold access to sensitive internal tools, and phishing-resistant security keys would have made the fake login page useless.
The 2022 Twilio Smishing Campaign
In mid-2022, the communications company Twilio was breached after attackers sent text messages to current and former employees, posing as IT and claiming their passwords had expired. The links led to fake Okta login pages on look-alike domains, and some staff entered their credentials.
Twilio’s own incident report notes a telling detail. The messages were convincing because the attackers had matched employee names to their phone numbers using outside data sources. That pairing is pure OSINT, and it is what put the right lure on the right phone.
Phishing-resistant multi-factor authentication is the control that holds here. A hardware security key cannot be handed to a fake page, so a stolen password on its own gets the attacker nowhere.
The 2023 MGM Resorts Attack
In September 2023, the group tracked as Scattered Spider profiled an employee of MGM Resorts from public sources, then called the IT help desk posing as that person and had a password and multi-factor token reset. The intrusion took systems offline across the business.
MGM told regulators in a securities filing that the incident would cost around 100 million dollars for the quarter. A joint advisory from CISA and the FBI later described the group calling help desks armed with personal details gathered from public sources to reset credentials and MFA.
The fix is unglamorous. A help desk must verify a caller with something an attacker cannot look up, such as a manager confirming in person or a callback to a number already on file.
OSINT, Awareness and Compliance
OSINT risk is not only an operational problem. In the EU it is now a legal one, because the rules that govern security put the human layer squarely in scope.
The EU NIS2 Directive, transposed into Swedish law as Cybersäkerhetslagen (SFS 2025:1506, in force 15 January 2026), lists security awareness training among its required measures under Article 21. The same article requires supply-chain security, which matters because attackers research your suppliers to reach you. Under Article 20 a company’s board is responsible for these measures and can be held personally accountable. See our guide to NIS2 compliance in Sweden for the full set of obligations.
The General Data Protection Regulation adds a second duty. The personal data your organisation publishes about staff is still personal data, and its principle of data minimisation applies to what you put online. A breach that exposes personal information must be reported to the Swedish authority IMY within 72 hours under Article 33. Our GDPR compliance in Sweden guide covers the detail.
For financial entities, DORA requires ICT risk management that covers these human-facing threats, supervised by Finansinspektionen. Awareness and verification controls are part of meeting it, as set out in our DORA compliance guide.
The EU AI Act adds oversight of automated profiling and AI systems, the same capabilities now used to scale OSINT and social engineering.
How to Spot OSINT-Driven Attacks
You will rarely catch the reconnaissance itself. It happens on public sites and in data you do not control, so it leaves almost no trace in your systems. MITRE makes the same point about its reconnaissance techniques. The detection effort belongs on the attacks that reconnaissance feeds, and those have tells.
These are the common signals to train people on.
- Urgency and secrecy: A request that pressures you to act fast and keep it quiet.
- A pretext built on real facts: The caller or sender knows your name, your manager or a current project, and uses that to lower your guard.
- A request that skips the normal process: A payment, a password reset or a data export that bypasses the usual checks.
- A channel that does not match: An executive who emails about money but never calls, or a text from a number you do not recognise.
- A look-alike domain: A web address that is almost right, with an extra word or a swapped letter.
Knowing the facts in a message does not make it genuine. The whole point of OSINT is that an attacker can know those facts too. Treat familiarity as the oldest trick, not as proof.
How to Shrink Your OSINT Attack Surface and Train Your People
Defending against OSINT means making yourself a harder and duller target. You cannot remove your public presence, but you can cut what it gives away and prepare your people for the attacks that get through. Work across three fronts.
People. Security awareness training is the core control, because the final step of almost every OSINT-driven attack is a person making a decision. Train staff on the real scenarios in this guide, rehearse the verification habit until it is automatic and make reporting a suspicious message quick and free of blame.
Process. Give the help desk an identity check that does not rely on knowable facts. Require out-of-band verification for payments and for any change to bank details. Apply least privilege so a single compromised account reaches as little as possible.
Technology. Deploy phishing-resistant multi-factor authentication, ideally hardware security keys, so a stolen password is not enough. Watch for look-alike domains that pair your name with words like login or sso. Keep software and exposed services patched and reviewed.
Then reduce the footprint itself. Audit your own organisation with the OSINT tools attackers use, and act on what you find. Keep software versions and internal tooling out of job adverts. Coach staff on what not to post. Set out-of-office replies that give nothing away.
If you take one habit from this guide, make it this. Verify any unusual or urgent request using a second channel you already trust, never the contact details in the message itself. That single step stops most of what OSINT sets up.